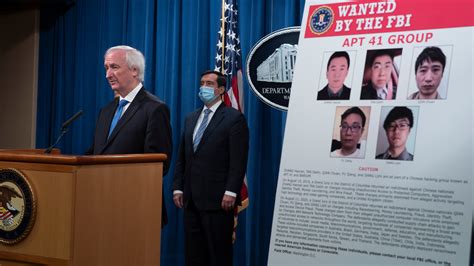
Chinese-linked hackers have allegedly been impersonating American artificial intelligence experts, including a former White House official, in a targeted cyberespionage campaign designed to obtain sensitive information about U.S. AI policymaking.
Cybersecurity firm Proofpoint revealed that a hacking group identified as TA419 has been attempting to steal passwords from individuals at American and Japanese think tanks, defense contractors, universities, and law firms since at least 2025.
Proofpoint attributed the activity to Chinese hackers based on malware, infrastructure, and targeting patterns consistent with Beijing’s intelligence priorities. The latest operation involved fraudulent emails appearing to originate from prominent AI and national security experts, including Lynne Parker, former principal deputy director of the White House Office of Science and Technology Policy.
These messages typically invited recipients to participate in AI-related projects or collaborations before directing them to fraudulent websites designed to steal login credentials. Among those targeted was Alex Engler, a former White House official who now leads the Penn Center on Media, Technology, and Democracy.
Engler said he received an email purportedly from Parker inviting him to participate in a new AI policy initiative. After noticing something suspicious and consulting colleagues, he discovered the message was fraudulent.
Proofpoint reported that the operation targeted fewer than 10 individuals across several organizations, particularly experts involved in AI regulation, export controls, and national AI strategy. The company’s findings indicate the hackers were pursuing intelligence about Washington’s policymaking rather than attempting to steal American technology.
Parker confirmed at least two individuals received suspicious messages using her identity in early July. “The United States and China are in a competition around AI,” Parker stated.